
 WhatsApp
API development and integration with clear failure handling
Growmoon helps you connect systems around an agreed data contract. Start with one source and destination. Define which records move, who owns each field and how your team can tell when a request succeeded, failed or needs review.
Identify the systems and any gaps in existing connectors
List the source and destination systems, their versions and the interfaces you can access. Check whether a supported connector meets the need. A missing field, approval step or timing rule helps define any custom work. Confirm the documentation, permissions, provider limits and a safe way to test before committing.
- List the systems, record types and intended direction of change.
- Identify what the current connector or manual process cannot handle.
- Confirm documentation, account ownership and test-environment access.
Document fields, identifiers and updates
For each record, identify required fields, stable identifiers, permitted states and transformations. Decide which system owns conflicting values and how updates are ordered. Timing also matters: an interactive request, a scheduled batch and an incoming event have different operating requirements. A field map should make these choices inspectable instead of leaving them inside assumptions about platform names.
Define accepted, rejected and uncertain outcomes
Agree what a response establishes and which saved result must be inspected. Receiving a request, accepting a record and delivering a later notification are different outcomes. A definite rejection differs from a lost response after a write may already have succeeded. Define how the caller or operator checks the existing result before repeating an operation that could create another record.
- Specify the expected stored result for an accepted request.
- Give invalid or unauthorized requests a clear failure outcome.
- Document reconciliation for an uncertain result.
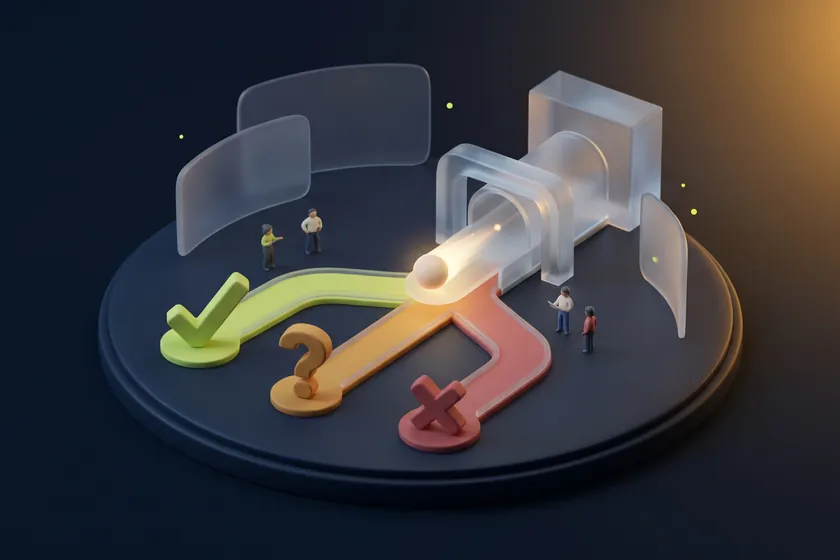
Test retries and failed requests
Requests can be repeated, delayed or delivered out of order. Agree when repeating the same operation is safe, which identifier represents the original event and how failures become visible. See the saved record from the API retry exercise. In Growmoon’s synthetic example, all ten local checks passed, including duplicate delivery and recovery after a simulated lost response. The exercise used SQLite and a fake notifier.
- Include a valid case, duplicate delivery and invalid input.
- Inspect denied access and a downstream timeout or partial failure.
- Record the expected outcome and evidence for the exact tested version.
Assign access, logging and operational ownership
Identify who controls accounts, credentials, permissions and environment configuration. Agree what logs must show so an operator can investigate a transfer without copying unnecessary sensitive data into them. Name responsibility for alerts, reconciliation, provider changes and support. Use an agreed secure channel for credentials; the project enquiry should contain documentation links and redacted examples instead.
Essential journey agreed
Meaningful exceptions included
Evidence ready to inspect
Compare takeover, repair and rebuild
For an existing integration, begin with source rights, build instructions, dependencies, known defects and available test access. The next step may be stabilization, a contained connector change or staged replacement. A dashboard, administrative interface or full application is not automatically part of API engineering. Compare these options against the actual problem and the responsibilities that must continue during a change.
Agree handover and ongoing costs
A scoped handover can identify interface documentation, mappings, configuration ownership, synthetic fixtures, actual test records, known limitations and recovery instructions. List the deliverables included in the agreement. Provider usage charges, hosting, monitoring and maintenance are separate cost and operating decisions. Specify review milestones and escalation responsibilities; an integration cannot promise control over a third party's uptime or future API changes.
Integration handover
- Interface contract
- Documentation and field mappings.
- Configuration
- Account, credential and environment ownership.
- Acceptance records
- Test records, limitations and recovery instructions.
- Operations
- Monitoring, maintenance and escalation responsibilities.
Questions about API integration
What evidence should an API integration handover contain?
Ask for the interface and field contract, authentication responsibilities, synthetic test inputs, observed saved results, safe logs and the exact tested revision. Include valid, rejected, repeated and uncertain outcomes with a recovery path. Agree hosting, credentials, maintenance and incident ownership separately.
Does a successful response prove that the whole journey completed?
It proves only what the receiving system's contract says it proves. Confirm the intended stored result and any later processing or notification separately. If a response is lost, reconcile the original request before assuming it failed or creating another record.
Is a dashboard or a complete application included in API development?
Not automatically. User interfaces, reporting, administrator tools, data migration and wider application work need their own scope. Start with the systems and journey to connect, then identify which additional features are actually required.
Walk us through one integration
Share the source and destination systems, versions, available documentation and the record you need to move. Describe one duplicate, timeout or recovery concern and who owns the existing accounts. Use redacted examples in the project message; arrange any required access separately through an agreed secure channel.
Discuss API integration scope